Search “best threat intelligence tools” and notice something before you read a single review: nearly every result is published by one of the vendors being reviewed, and that vendor consistently ranks itself first. Cyble’s list puts Cyble Vision at #1. CloudSEK’s list puts CloudSEK at #1. Flare’s list puts Flare at #1. This isn’t necessarily dishonest — these companies may genuinely believe their own product is best — but it means almost none of the “top 10” content in this space is actually independent, and that’s worth knowing before you trust any single ranking, including implicitly trusting whichever platform happens to have the most aggressive content marketing team.
Here’s what threat intelligence tools actually do, the real categories most comparisons blur together, and how to evaluate this category without leaning on a vendor’s opinion of itself.
What Threat Intelligence Tools Actually Do
Cyber threat intelligence (CTI) tools collect, analyze, and operationalize data about active threats — malicious actors, their tactics, leaked credentials, malware campaigns, ransomware activity, and exposed infrastructure — so security teams can detect and respond before damage occurs. Modern platforms pull from the clear web, dark web forums, Telegram channels, stealer log markets, ransomware leak sites, and open-source feeds, then enrich that raw data and feed it into a security team’s existing SIEM, SOAR, or analyst workflow. The stakes behind this category are real and rising: according to IBM’s X-Force Threat Intelligence Index, infostealer phishing emails rose 84% year over year, with 70% of attacks targeting critical infrastructure specifically.
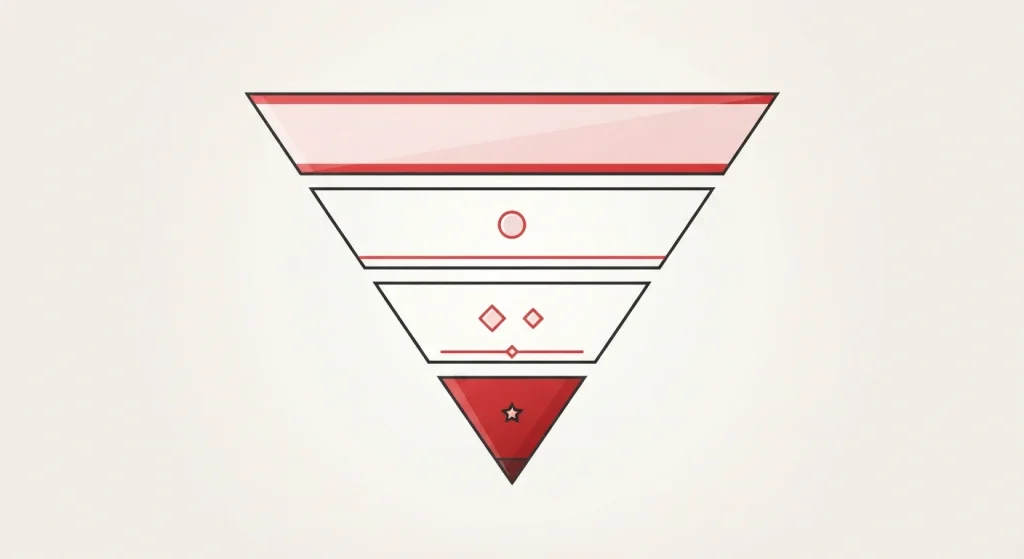
The Four Real Types of Threat Intelligence
Most vendor comparisons skip this framework entirely and jump straight to product features, but understanding it first is what actually determines which product category you need.
Strategic Intelligence
High-level, non-technical analysis aimed at executives and decision-makers — trends in attacker motivations, geopolitical risk factors, and industry-wide threat patterns that inform budget and policy decisions rather than day-to-day defense.
Tactical Intelligence
Information about specific attacker techniques, tactics, and procedures (often referenced against frameworks like MITRE ATT&CK) — useful for security teams building detection rules and defensive playbooks against known attacker behavior patterns.
Operational Intelligence
Details about specific, often imminent threats — a planned campaign, an active ransomware group’s current targeting pattern — giving defenders actionable warning ahead of an attack rather than after one.
Technical Intelligence
The most granular layer: specific indicators of compromise (IOCs) — malicious IP addresses, file hashes, domain names — that plug directly into automated security tooling for real-time blocking and detection.
Most commercial platforms cover pieces of several of these categories simultaneously, but their actual strength usually concentrates in one or two — which is exactly why matching a specific need to a specific category matters more than a vendor’s overall marketing positioning.
Free and Open-Source Options Worth Knowing About
This is the part self-published vendor rankings have the least incentive to emphasize, since it doesn’t lead to a sale, but it’s genuinely useful for smaller teams or anyone starting out in this space.
- MISP (Malware Information Sharing Platform) is a genuinely capable open-source threat intelligence sharing platform, widely used across security research communities for collaborative IOC sharing without licensing cost.
- Have I Been Pwned offers free breach notification lookups, with paid options for organizations needing broader monitoring — a legitimate, narrowly-scoped free tool rather than a full platform.
- LevelBlue Open Threat Exchange (formerly AlienVault OTX) provides free, community-driven IOC sharing, a reasonable starting point for smaller security teams without budget for a commercial platform.
None of these free options replace a full enterprise threat intelligence platform’s automation, enrichment, and dedicated analyst support — but they’re a genuinely reasonable starting point, and worth trying before committing budget to a commercial platform, particularly for smaller organizations still defining their actual needs.
What Separates Commercial Platforms From Each Other
Rather than ranking specific vendors — which, given the bias problem above, isn’t something worth doing credibly in a single article — it’s more useful to understand the real axes commercial platforms actually differentiate on:
Intelligence source breadth
Some platforms specialize heavily in dark web and closed-forum monitoring; others focus on IOC feed volume and correlation; a newer category, identity intelligence, focuses specifically on leaked credentials and stealer logs rather than traditional indicators.
Integration depth
How deeply a platform plugs into your existing SIEM, SOAR, and ITSM tooling determines whether intelligence actually reaches the people who act on it, or sits in a separate dashboard nobody checks regularly.
Automation and enrichment quality
The genuinely useful differentiator in 2026’s market isn’t raw feed size — it’s how well a platform automatically prioritizes and contextualizes what actually matters out of an otherwise overwhelming volume of raw threat data.
Analyst usability
A platform an analyst actually wants to use daily delivers more real value than one with a longer feature list that ends up under-adopted — this is a genuinely underrated evaluation criterion buried under most vendor comparisons’ feature checklists.
How to Actually Evaluate This Category Yourself
| Your situation | Reasonable starting point |
|---|---|
| Small team, limited budget, just starting | MISP or LevelBlue OTX (free/open-source) |
| Need executive-level strategic reporting | Look for platforms with strong analyst-authored strategic reports, not just raw feeds |
| Already invested heavily in a specific EDR/XDR ecosystem | Consider that platform’s native threat intelligence module first for integration simplicity |
| Need deep dark web/closed-forum visibility specifically | Prioritize platforms explicitly built around that source type over general IOC aggregators |
| Evaluating any vendor’s own comparison content | Weight it as marketing, not independent research — check third-party sources like Gartner or Forrester analyst positioning separately |
Frequently Asked Questions
What is the difference between a threat intelligence platform and a SIEM?
A SIEM aggregates and analyzes security event logs from within your own environment. A threat intelligence platform brings in external context — information about active threats, attacker behavior, and indicators of compromise from outside sources — which often feeds into a SIEM rather than replacing it.
Are free threat intelligence tools actually useful, or just limited demos?
Genuinely useful, within scope — tools like MISP and LevelBlue OTX are real, actively maintained platforms used by real security teams, not stripped-down trials. They simply cover a narrower scope than a full commercial platform’s automation and enrichment capabilities.
Why do all the “best threat intelligence tools” articles rank different platforms first?
Because the overwhelming majority of this content is published directly by the vendors being ranked, each naturally placing itself first — worth checking who published any given “best of” list before treating its top pick as independent judgment.
What’s identity intelligence, and how is it different from traditional threat intelligence?
It’s a newer category focused specifically on leaked credentials, stealer logs, and compromised identity data, driven by the sharp rise in infostealer malware — a complement to traditional IOC-focused intelligence rather than a full replacement for it.
Do I need a paid threat intelligence platform if I’m a small organization?
Not necessarily to start — free and open-source options can meaningfully cover early-stage needs. Growing threat exposure, regulatory requirements, or the volume of alerts needing triage are the more common signals it’s time to evaluate a paid platform.
The most useful thing you can bring to evaluating this category isn’t a ranked list — it’s the specific question of what type of intelligence your team actually needs, at what maturity level, and skepticism toward any comparison written by someone with a product in the running.